The system of record for security and compliance
Inventory, controls, evidence, vendors, and audits in one place. Built so proving your posture is a byproduct of running it.
NewAutomated evidence checks
Compliance work is mostly evidence work. Cyberwiz keeps evidence current, tied to the control it proves, and ready the moment someone asks for it.
Purpose-built
Shaped around how security teams actually work: controls, evidence, vendors, and the auditors who ask.
Powered by AI
Documents are read, matched to the control they prove, and scored: conclusions, not files.
Always current
Evidence expires, integrations refresh, and controls re-check themselves, not once a year.
What Cyberwiz does
Everything you run, found for you
Cloud accounts, repositories, instances, devices and buckets, found by your integrations or added by hand. Define your own kinds. Every control and vendor question hangs off it.
Learn moreAll assets
Everything this organization owns and has to harden, whether an integration found it or somebody entered it. Systems, processes and data repositories keep their own tabs.
Adopt a framework, not a spreadsheet
ISO 27001, SOC 2, NIST 800-53, PCI DSS, HIPAA, GDPR, and NIS2 ship mapped to one shared control set. Satisfy a control once and every framework that asks for it moves.
Learn moreYour frameworks (4)
ISO 27001v2022
The information security management standard. Certifiable, and the one buyers ask for by name.
SOC 2 Type 2v2017 TSC
Trust services criteria, reported on over a window rather than a moment.
Evidence that checks itself
Connect a system or upload a document. Cyberwiz reads it, matches it to the control it proves, scores the result, and flags it when it goes stale.
Learn moreActive
21
Pending
1
In grace
2
Archived
0
Policies that count for something
Write the policy in the product, route it for approval, and publish it. Publishing emits evidence against the controls it answers for, so readiness moves without an upload.
Learn morePurpose
You cannot protect what you cannot see. Access reviews, vulnerability management, change control and incident response all begin by asking which systems exist and who is responsible for them, and every one of them is only as complete as the answer.
This policy sets out how the organization identifies its information assets, records them, assigns ownership of them, and manages them from acquisition through to disposal.
Scope
Applies to all employees, contractors and third parties who acquire, operate, hold or dispose of an asset on behalf of the organization. It covers end-user devices, servers, containers, databases, and the accounts, domains and cryptographic keys that make them reachable.
Roles and responsibilities
The policy owner owns the asset register as a whole and is accountable for its completeness. Asset owners are accountable for the individual assets recorded against their name.
The asset register
Every asset is recorded in a single register, whether a connector discovered it or a person entered it by hand. A record carries the asset’s name, its kind, its owner, its classification and its lifecycle state, and no record is complete without all five.
Classification
Every asset is classified when it is recorded and reclassified when what it holds changes. The classification decides what protection it gets, so an unclassified asset is treated as the most sensitive one it could be until somebody says otherwise.
Disposal
An asset leaves the register only once whatever it held has been destroyed or returned, and the record of its disposal outlives the asset itself.
Run vendor due diligence end to end
Send a questionnaire, chase the answers, score the findings, and track remediation. Vendors answer in their own portal, in their own language.
Learn moreWelcome, Bindsec 👋
Here are your security assessment results for “Basic Vendor Security Assessment”, requested by Vertex Labs.
1. Organizational profile
1.1 Nature and purpose of the engagement
1.1.1 What services does your organization provide to the client?
Choose the option that best matches.
1.2 IT services
1.2.1 Which specific IT services does your organization provide?
Depends on Q1.1Select every service that applies.
Contents
- 1. Organizational profile
- 2. Data centre profile
- 3. Secure development (SSDLC)
- 4. Governance and compliance
- 5. Access control
- 6. Human resources
- 7. Communications
- 8. Network security
- 9. Endpoint security

Give auditors a scoped view, not your account
Invite an auditor to specific frameworks and dates. They review controls and evidence in place, and leave with a Statement of Applicability.
Learn moreAnswer the security questionnaire before it is sent
Publish your frameworks, monitored controls, policies and subprocessors to a trust center on your own domain. Keep the SOC 2 behind an access request and an NDA, and see who asked for what.
Learn moreBindSec Trust Center
Security and compliance, generated from our live programme and republished whenever it changes. Every figure below is the one our own auditors were shown.
The policies the programme is run against, published at the version your auditor saw.
Monitored continuously against the systems they cover. 128 passing, 6 outstanding.
Everyone who touches customer data, with the region they hold it in.
Every finding lands on a board
Gaps, reviews and remediations become tasks with an owner, a priority and a due date. Scheduled access reviews open their own when they come due.
Learn moreQuarterly access review: AWS production accounts
Pull every IAM user and role on the prod account and reconcile the entitlements against the joiner-mover-leaver record before the quarter closes.
Created 12 Apr
Collect the renewed SOC 2 report from Datadog
The report on file expires 30 Apr. Request the new one and the bridge letter ahead of the contract renewal review.
Created 12 Apr
Write up the backup restore test for A.8.13
February's restore drill ran without a written record, so the control has no evidence behind it. Capture the runbook, the result and the sign-off.
Created 13 Apr
Remediate A.5.1, three policies past their review date
Information security policies is failing at 43% readiness because the acceptable use, remote work and encryption policies are all overdue their annual review.
Created 8 Apr
Bring the last 12 admin accounts under SSO and MFA
Secure authentication (A.8.5) sits at 91% while these accounts authenticate outside the identity provider policy.
Created 9 Apr
Chase Acme Payments on the outstanding assessment
The questionnaire went out 14 days ago with no response. Escalate to the vendor owner before the contract review on the 25th.
Created 9 Apr
Review the evidence package for A.5.15 Access control
Eight files uploaded by the platform team; two failed the reviewed-within-required-period validation and need re-signing.
Created 5 Apr
Duplicate findings on the vulnerability scan import
March's scan imported twice, so A.8.8 counts 36 open findings where the scanner reported 18. De-duplicate and re-run the readiness calculation.
Created 7 Apr
Walkthrough pack for the ISO 27001 auditor engagement
Scope, control list and the evidence index assembled for the external auditor's opening meeting. With Adi for sign-off.
Created 3 Apr
See drift before your auditor does
Dashboards, tasks, and weekly digests keep the work moving between audits. Readiness becomes a number you watch, not a scramble you survive.
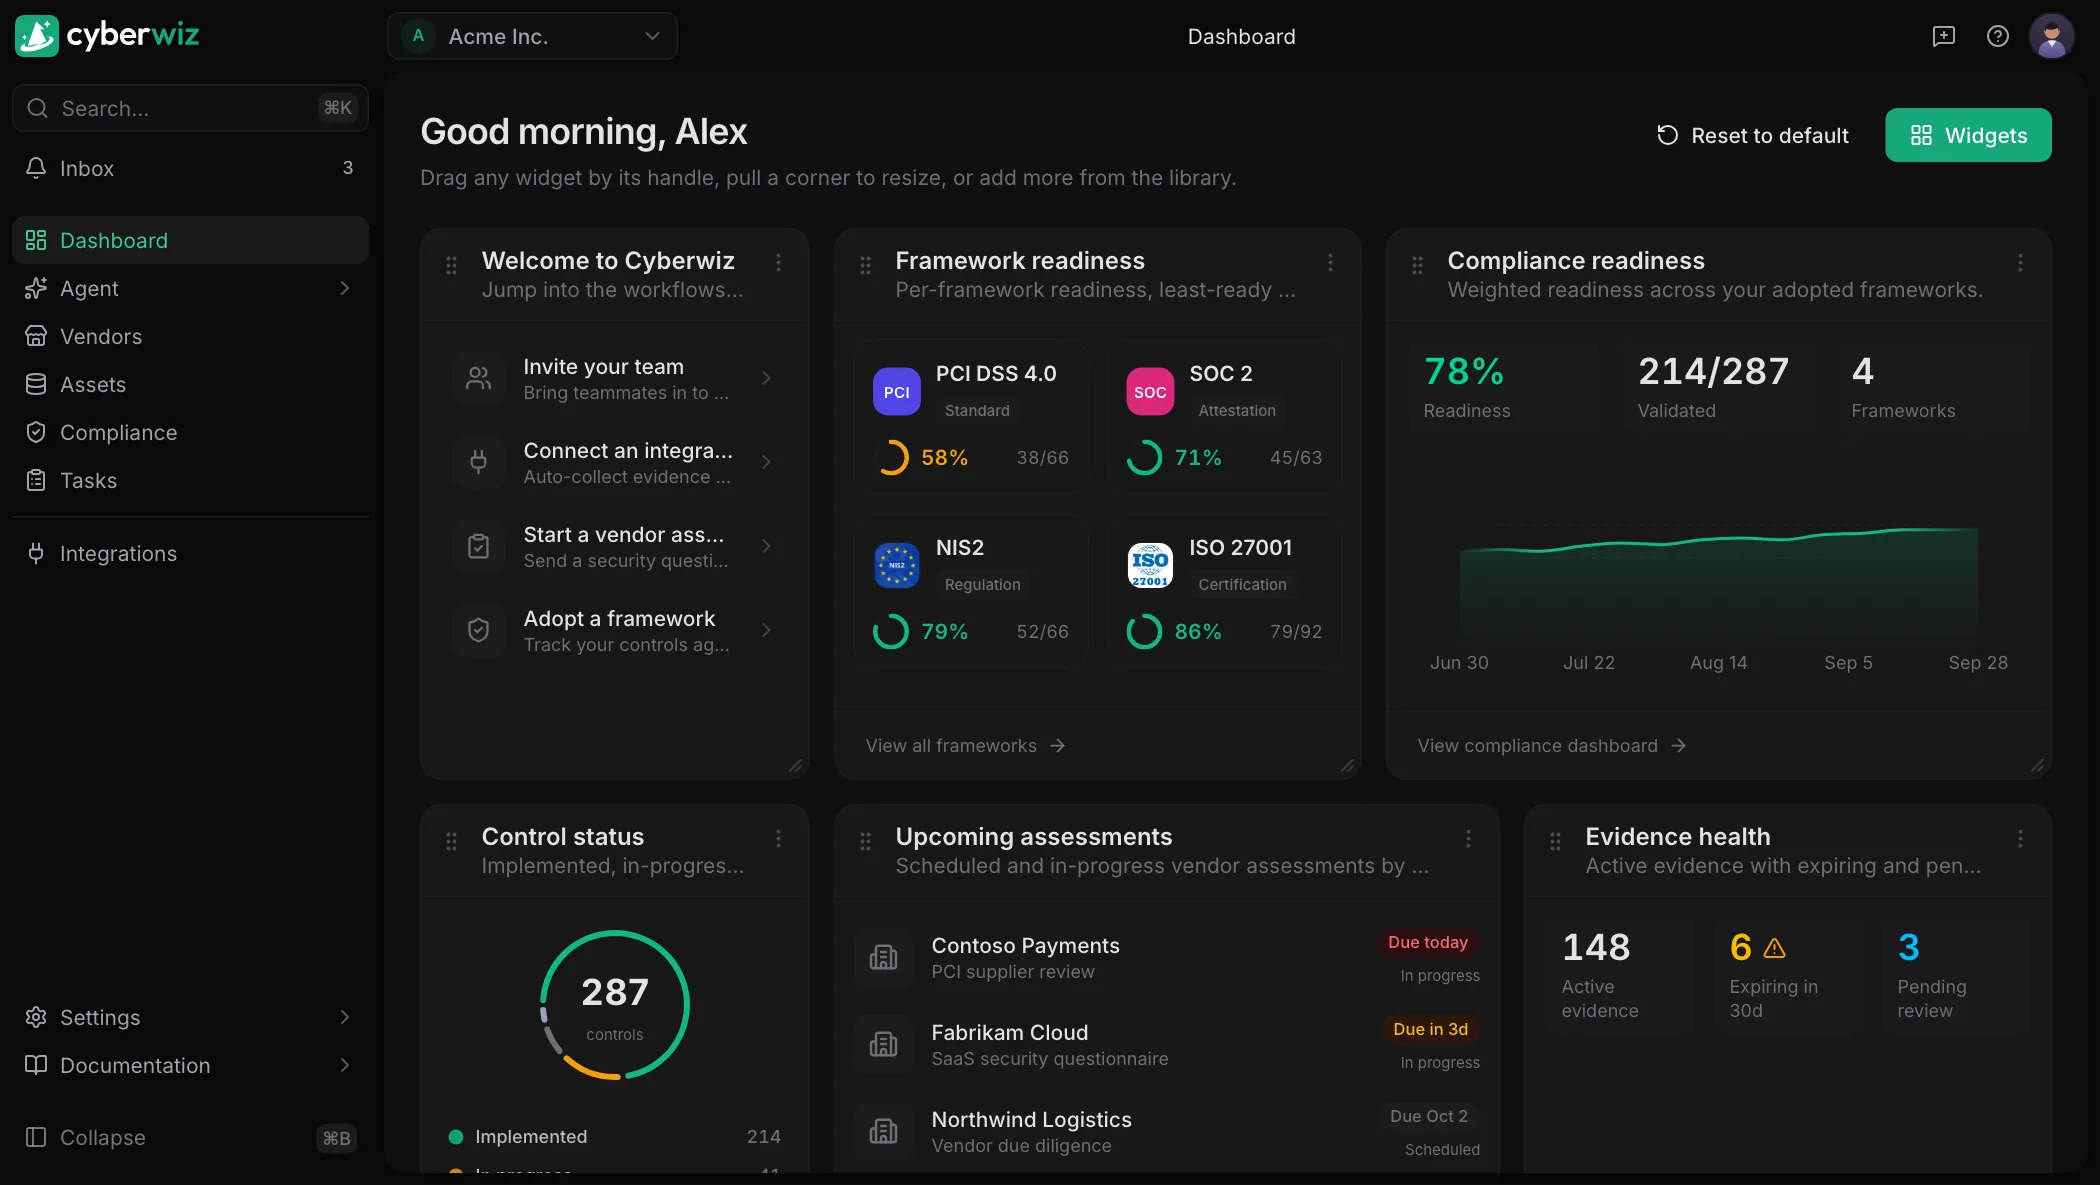
Learn moreFramework readiness
Per-framework readiness, least-ready first.
PCI DSS 4.0
SOC 2
NIS2
ISO 27001
Evidence health
Active evidence with expiring and pending-review counts.
Active evidence
Expiring in 30d
Pending review
Weighted readiness across 4 frameworks, last 90 days
6 items expire within 30 days
Upcoming assessments
Scheduled and in-progress vendor assessments by due date.
- Contoso PaymentsPCI supplier reviewIn progressDue today
- Fabrikam CloudSaaS security questionnaireIn progressDue in 3d
- Northwind LogisticsVendor due diligenceScheduledDue Oct 2
An agent that asks before it writes
It reads your vendors and your asset register, and answers how the product works from the documentation. Every create, update and delete stops at a card showing exactly what it is about to change.
Learn moreLooked up vendors
Three of your twelve, and one is overdue:
Contoso Payments, due today
Acme Cloud, due in 3d
Northwind Logistics, scheduled
Read the documentation
Vendors → Add vendor. Name and type are the only required fields; criticality, owner and contacts can follow later.
Or tell me the name and I will create it for you.
Managed service
Or have the whole program run for you
Bindsec runs vendor due diligence and compliance operations on Cyberwiz: vendor communication, evidence review, and reporting. Same platform, none of the operating load.
Managed serviceBuilt for the people who own the answer
Security & GRC
Proving a framework holds, continuously, and knowing the moment it stops holding.
Procurement & vendor management
Clearing third parties without a spreadsheet chain or a mailbox full of attachments.
Auditors & consultants
Working across client programs from one scoped view, with the evidence already in order.
Changelog
A real questionnaire builder, and notifications you set
Questionnaires get a drag-and-drop builder with a live preview and logic that survives renaming, and notification settings split into categories, a priority inbox and a weekly digest.
Google Workspace, OneLogin, and evidence that bundles
Two more identity sources collect evidence on their own, evidence files combine without losing the originals, and the app gained a What's new panel.
Trust, people, and policies that read themselves
A public Trust Center, a register of the people behind every account, and an import that suggests the controls a policy covers.
The policy page, rebuilt
Policies get tabs, a version picker and a real list, and the copilot stops refusing the follow-up.
Provable today, not at audit time.
Run it yourself or have Bindsec run it for you. Either way, the evidence is current and the posture is one place.